Microsoft is testing Remote Lock, an Intune feature that blocks access to managed Windows PCs without deleting their files. The preview appeared on November 13 in Windows 11 Insider Preview Build 29708.1001, in the Experimental (Future Platforms) channel.
Once locked, a PC cannot be opened with a password, PIN, local administrator account or web sign-in. IT must send an unlock instruction through Intune, even if the employee has recovered the laptop.
The feature gives organisations an alternative to wiping a missing device. However, both locking and unlocking depend on the PC checking in with Intune. An offline laptop will not receive either instruction until it reconnects.
What happens to a locked PC
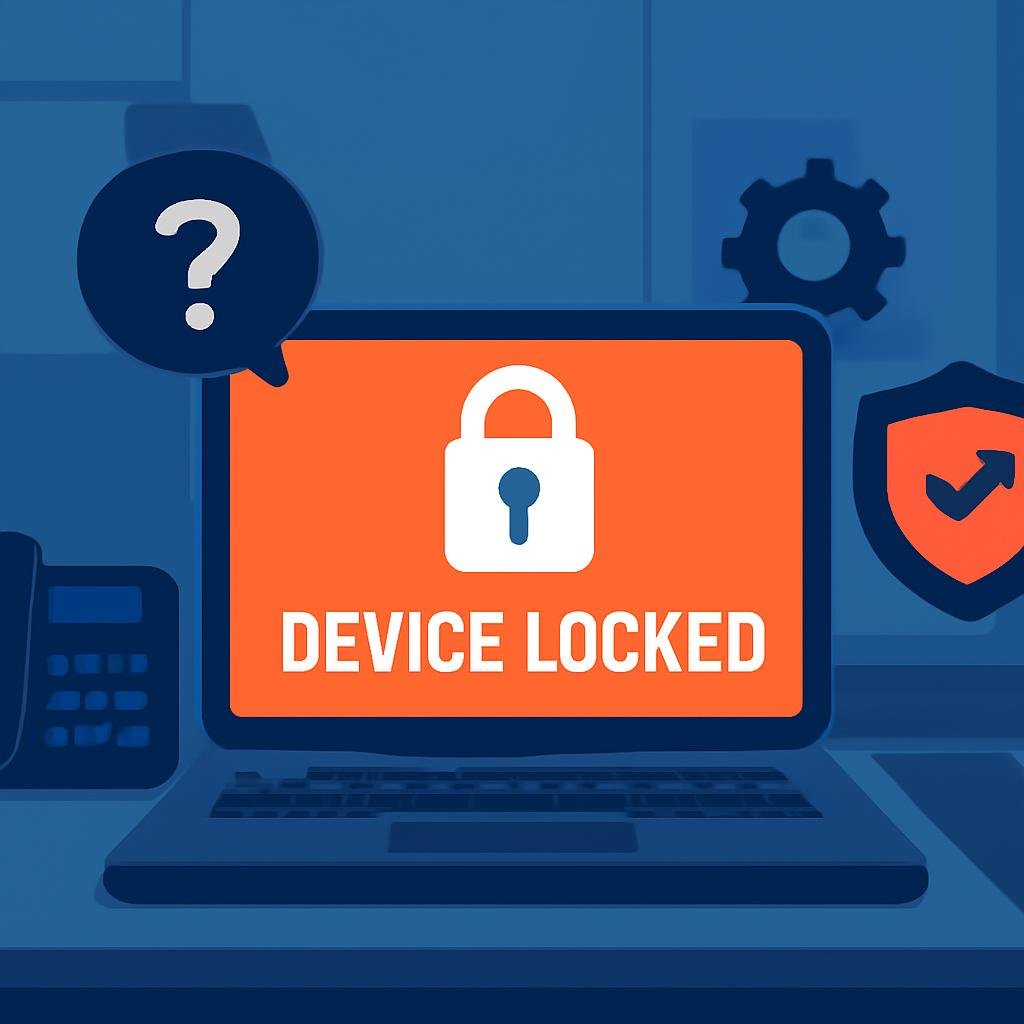
Remote Lock ends every active Windows session and removes the usual sign-in choices. Instead, Windows displays a Device Locked screen directing the user to IT support.
Administrators can customise that screen with a reason for the lock and help desk details. The default message reads, “Your organization has locked this device”.
Microsoft says files stay in place, BitLocker remains enabled, and the device stays enrolled in Intune. “Nothing is erased,” the company says in its release notes.
Restarting the computer or disconnecting it from the internet does not remove an existing lock.
The restriction applies to the device, not the employee’s account. The same credentials will still work elsewhere. If an account is compromised, IT must separately disable it or revoke its sessions in Microsoft Entra ID.
How administrators apply the lock
For this preview, administrators must use a custom configuration profile rather than Intune’s existing Remote lock button. That button currently supports Android, iOS/iPadOS, macOS and visionOS, but not Windows.
Microsoft’s documentation lists Windows Pro, Enterprise and Education as eligible editions. Devices must be Microsoft Entra joined, hybrid joined or enrolled in mobile device management.
The documentation also names Windows 10 and Windows Server 2016, 2019, and 2022. So far, however, Microsoft has announced Remote Lock only for this Windows 11 preview build.
In the Intune admin center, administrators start at Devices > Windows > Configuration > Create > New policy. They select Windows 10 and later, then Templates > Custom, and configure these OMA-URI settings:
| Setting | OMA-URI | Value |
|---|---|---|
| Lock state, required | ./Device/Vendor/MSFT/RemoteDeviceLock/LockState | Integer: 1 to lock; 0 to unlock |
| Lock reason, optional | ./Device/Vendor/MSFT/RemoteDeviceLock/LockReason | Up to 1,024 characters |
| Recovery hint, optional | ./Device/Vendor/MSFT/RemoteDeviceLock/RecoveryHint | Up to 256 characters |
IT assigns the locking profile to a dedicated device group, with LockState set to 1. Adding a computer to that group applies the restriction at its next check-in.
Restoring access requires a second profile with LockState set to 0, assigned to an unlock group. IT then moves the device into that group.
A read-only Status node reports four possible states: Unlocked (0), Locked (1), Lock pending (2), or Error state (3).
BitLocker still protects the files
Remote Lock prevents normal sign-in, but it does not disconnect the computer from the network. It also leaves Windows Recovery Environment, Safe Mode and USB boot available.
Microsoft warns that someone with physical access could still remove the drive or reimage the computer. The company therefore says BitLocker should remain enabled to protect stored data.
The preview marks a change from Microsoft’s stated position in March 2025. At an Intune event, Microsoft’s Joe Lurie said, “We do not have plans today to implement Remote Lock on Windows devices.” Another Microsoft employee said the feature was not high on the team’s backlog.
Roughly 20 months later, Windows Remote Lock is available for early testing, rather than general deployment.